Infrastructure
This guide covers how to create and manage infrastructure in GoInfra. An Infra is an instance of your cloud provider that allows you to create and manage virtual machines (or Kubernetes clusters) for your blockchain organization.
- Accessing GoInfra
- Choosing a Provider
- Creating an External provider
- Creating an Amazon Web Services provider
- Creating a Google Cloud Platform provider
- Creating a Microsoft Azure provider
- Creating an AWS EKS provider
- Choosing the Open Ports
- Managing an Infra
- Next Steps
Accessing GoInfra
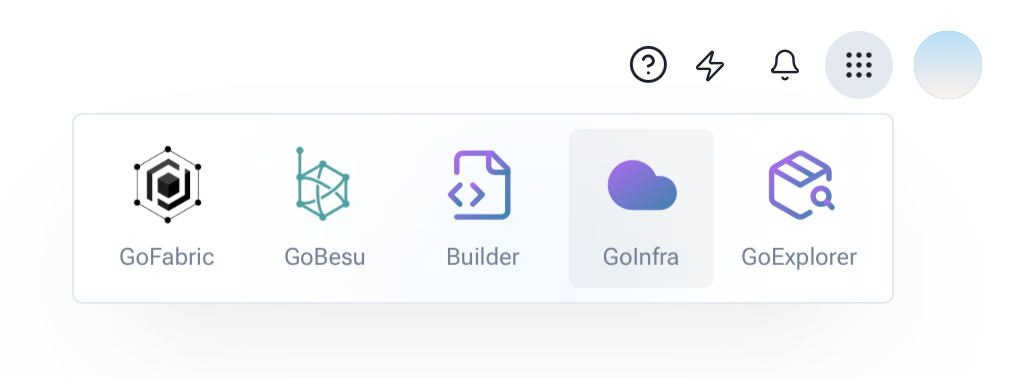
Access GoInfra by clicking on the App Menu in the navigation bar and selecting GoInfra.
On the overview page you will see all the infrastructures you have already created. To create a new one, click the + New Infra button in the top right corner.
Choosing a Provider
After clicking + New Infra (or navigating to Create Infra in the sidebar), you will be prompted to select a cloud provider for your infrastructure.
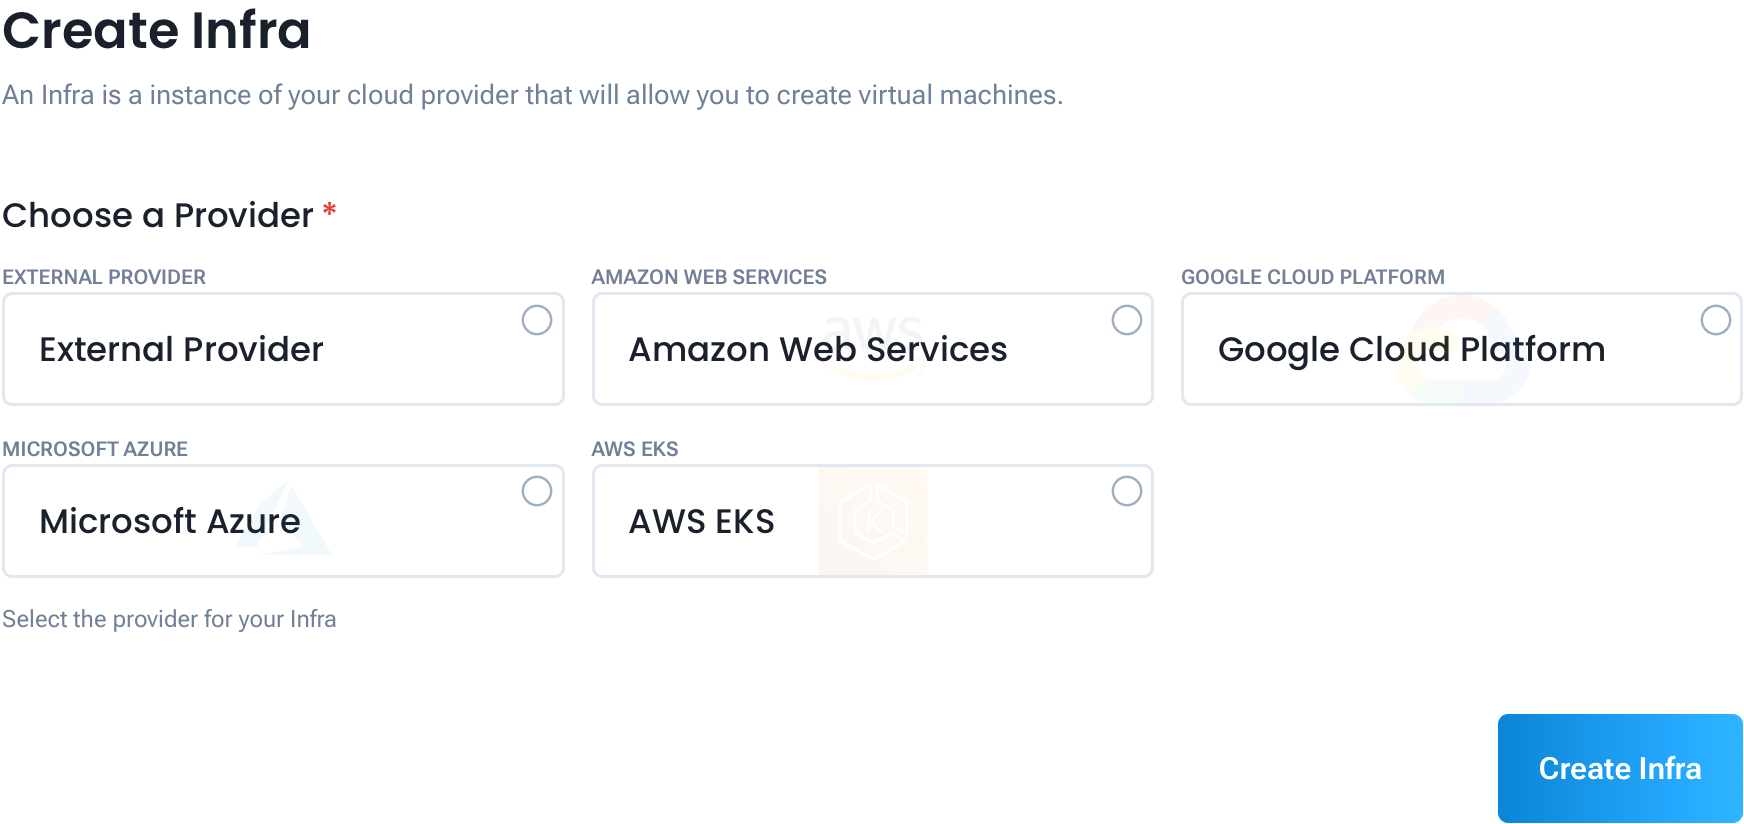
The available providers are:
| Provider | Infrastructure type | Availability |
|---|---|---|
| External Provider | User-managed VMs connected via SSH | Starter and above |
| Amazon Web Services | EC2 virtual machines managed by GoInfra | Higher-tier plans |
| Google Cloud Platform | GCP virtual machines managed by GoInfra | Higher-tier plans |
| Microsoft Azure | Azure virtual machines managed by GoInfra | Higher-tier plans |
| AWS EKS | Kubernetes cluster on Amazon Elastic Kubernetes Service (GoFabric) | Higher-tier plans |
ℹ️ Note: GoBesu networks run on virtual machines (External, AWS, GCP or Azure). AWS EKS is shown as Coming soon in the GoBesu flows.
Select the provider that matches your setup and fill in the details below.
Creating an External Provider
The External provider lets you connect your own pre-existing machines to GoInfra using SSH. GoInfra will not provision or manage the underlying VMs — you are responsible for the machines.
Select External Provider and fill in the following:
Infra Details
- Name (required): A name to identify your infrastructure within GoChain.
Then click Create Infra.
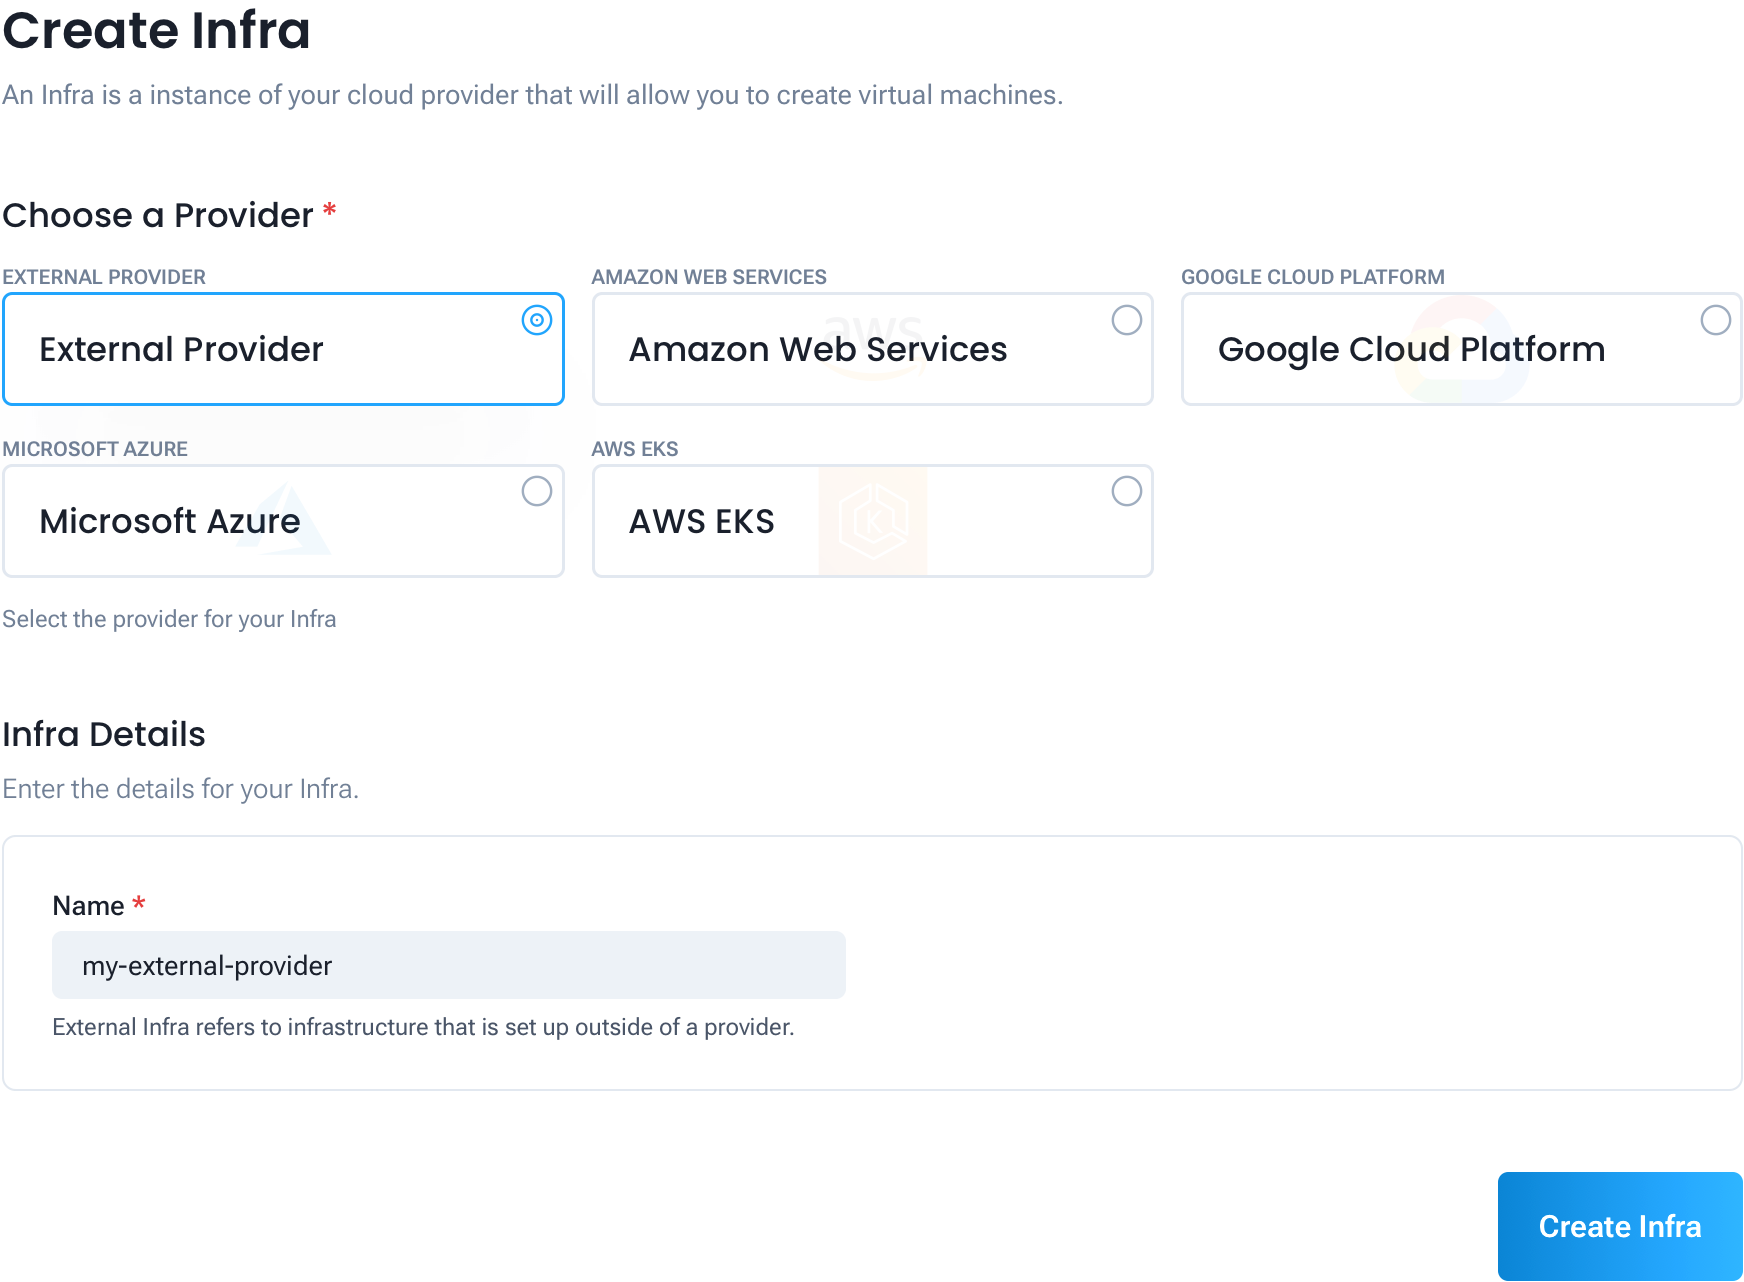
After the infra is created, you will be taken to the VM setup step where you can register your existing machines. See the VM Setup Guide for details.
Creating an Amazon Web Services Provider
The AWS provider lets GoInfra create and manage EC2 instances directly in your AWS account.
Select Amazon Web Services and fill in the following:
Infra Details
- Name (required): A name to identify your infrastructure.
- Region (required): The AWS region where your VMs will be created (e.g.
us-east-1). - Access Key (required): Your AWS IAM Access Key ID.
- Secret Key (required): Your AWS IAM Secret Access Key.
Security Group
- Security Group Name (required): The name of the AWS security group GoInfra will create. This name must not already exist in your AWS account — GoInfra will create it with the required firewall rules for the blockchain components.
- Security Group Description (required): A short description for the security group.
Create Private Key
- Key Name (required): The name of the SSH key pair GoInfra will create in your AWS account. This name must not already exist in your account.
- Key Description (required): A short description for the key pair.
Open ports
- Choose what will run on the virtual machines, so the firewall opens the right ports. See Choosing the Open Ports.
Then click Create Infra.
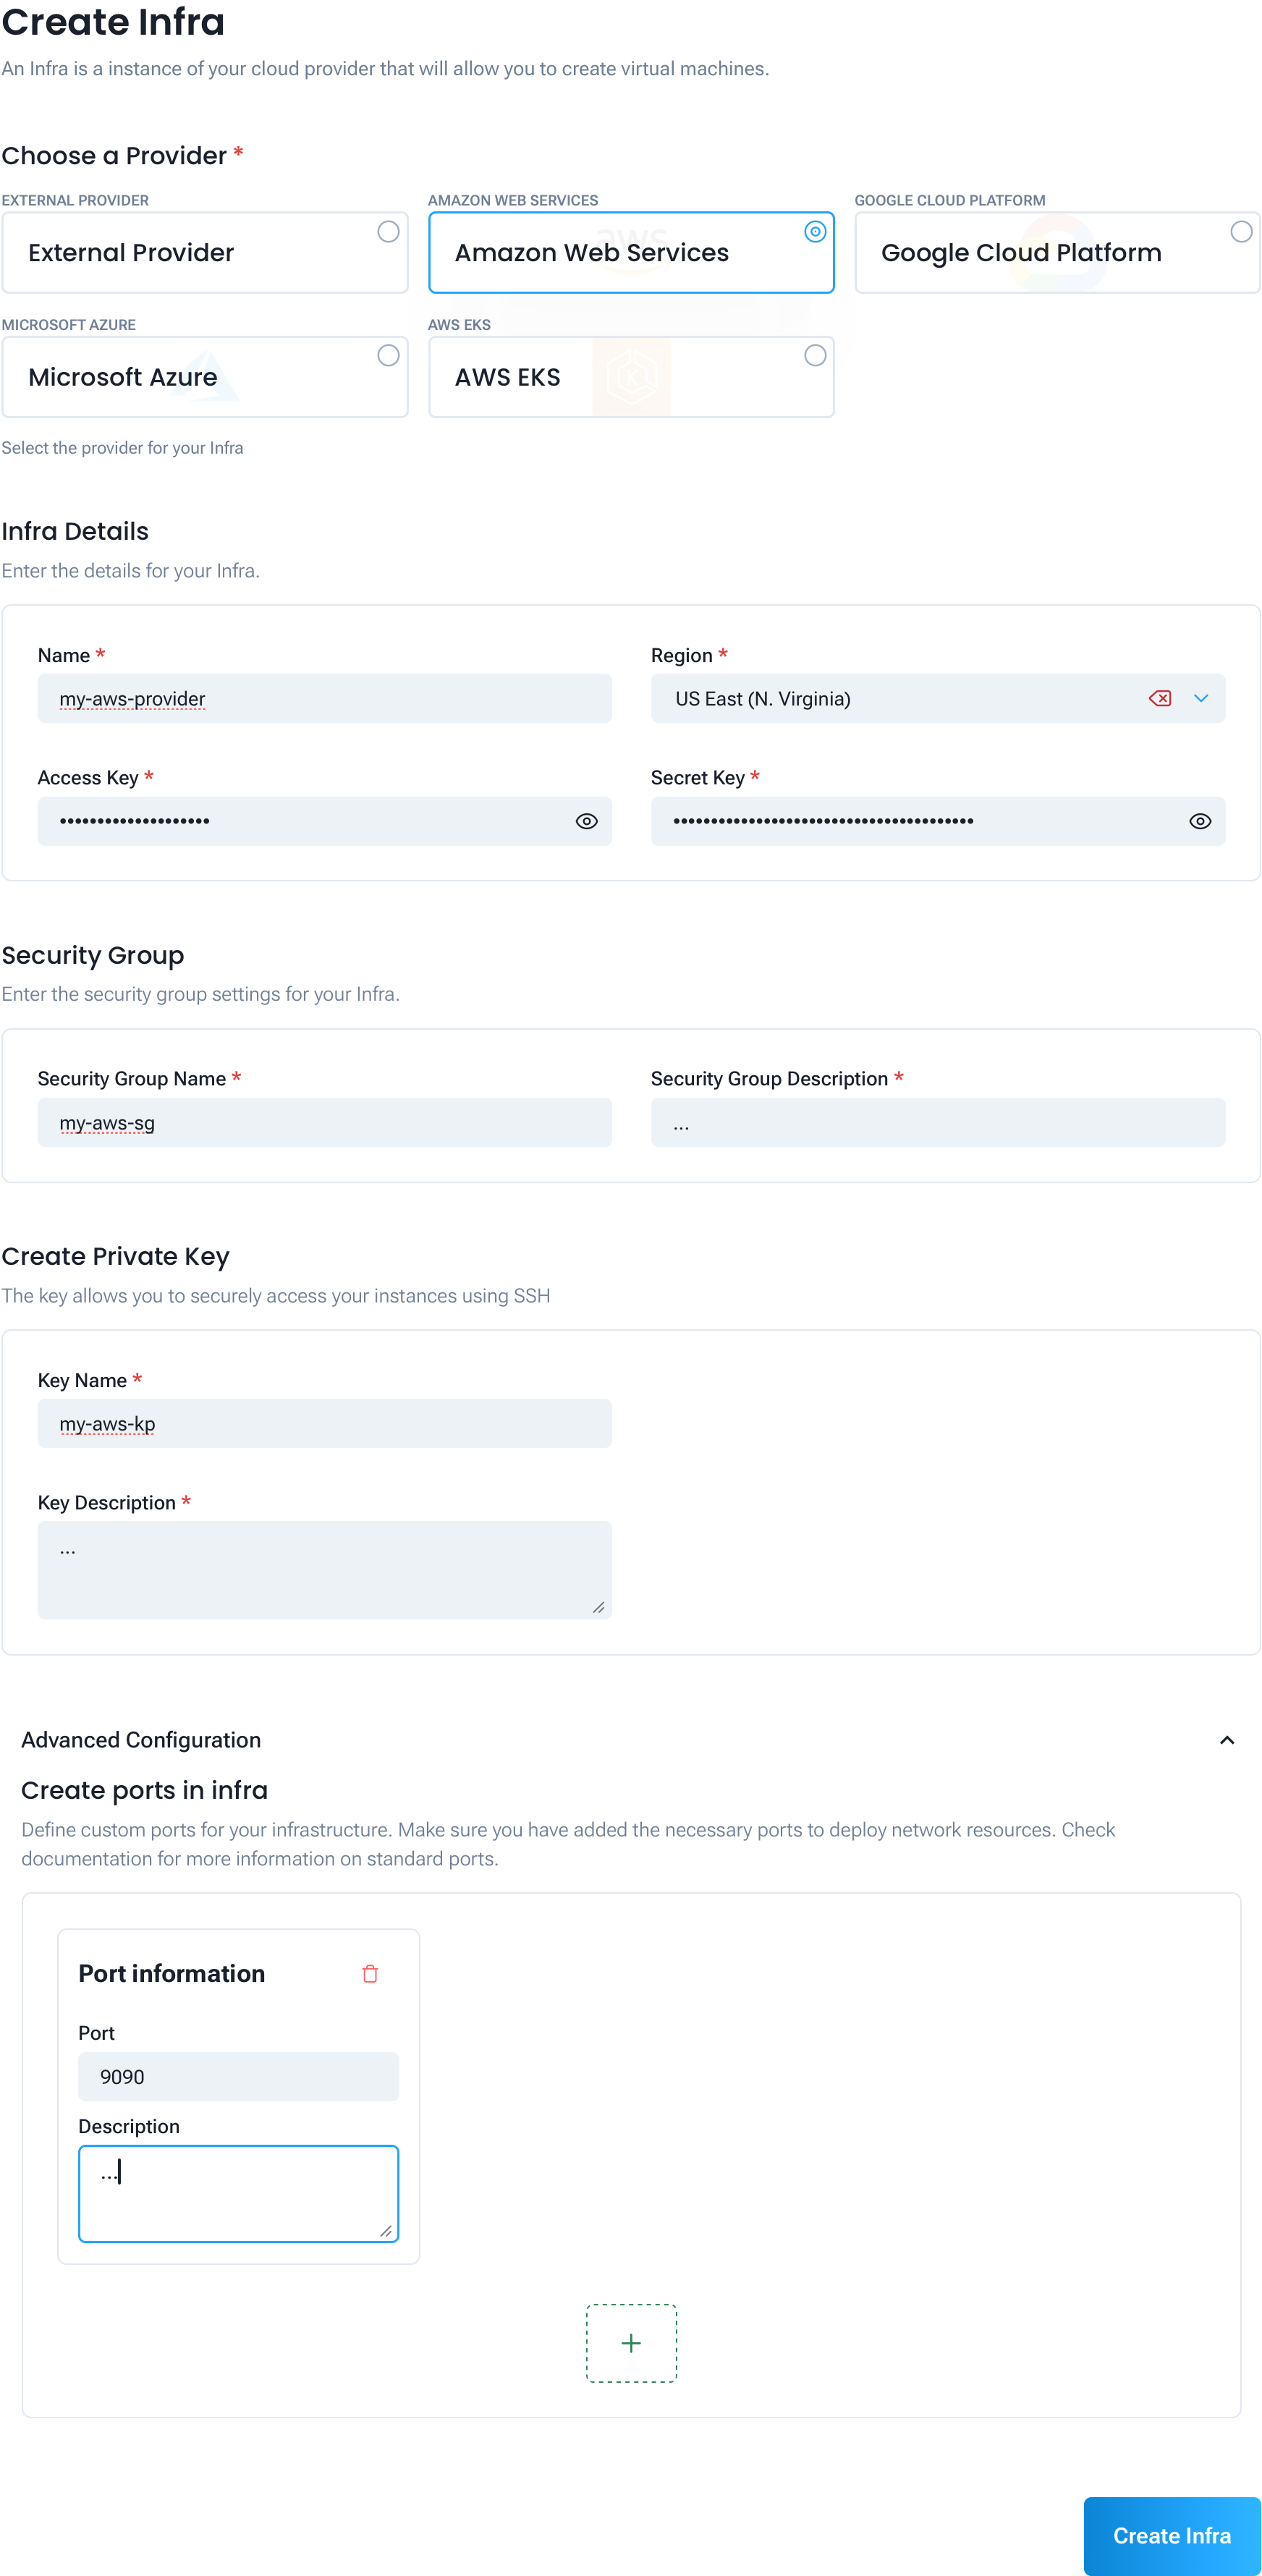
After the infra is created, you will be taken to the VM setup step. See the VM Setup Guide for details.
Creating a Google Cloud Platform Provider
The GCP provider lets GoInfra create and manage virtual machines in your Google Cloud project using a service account.
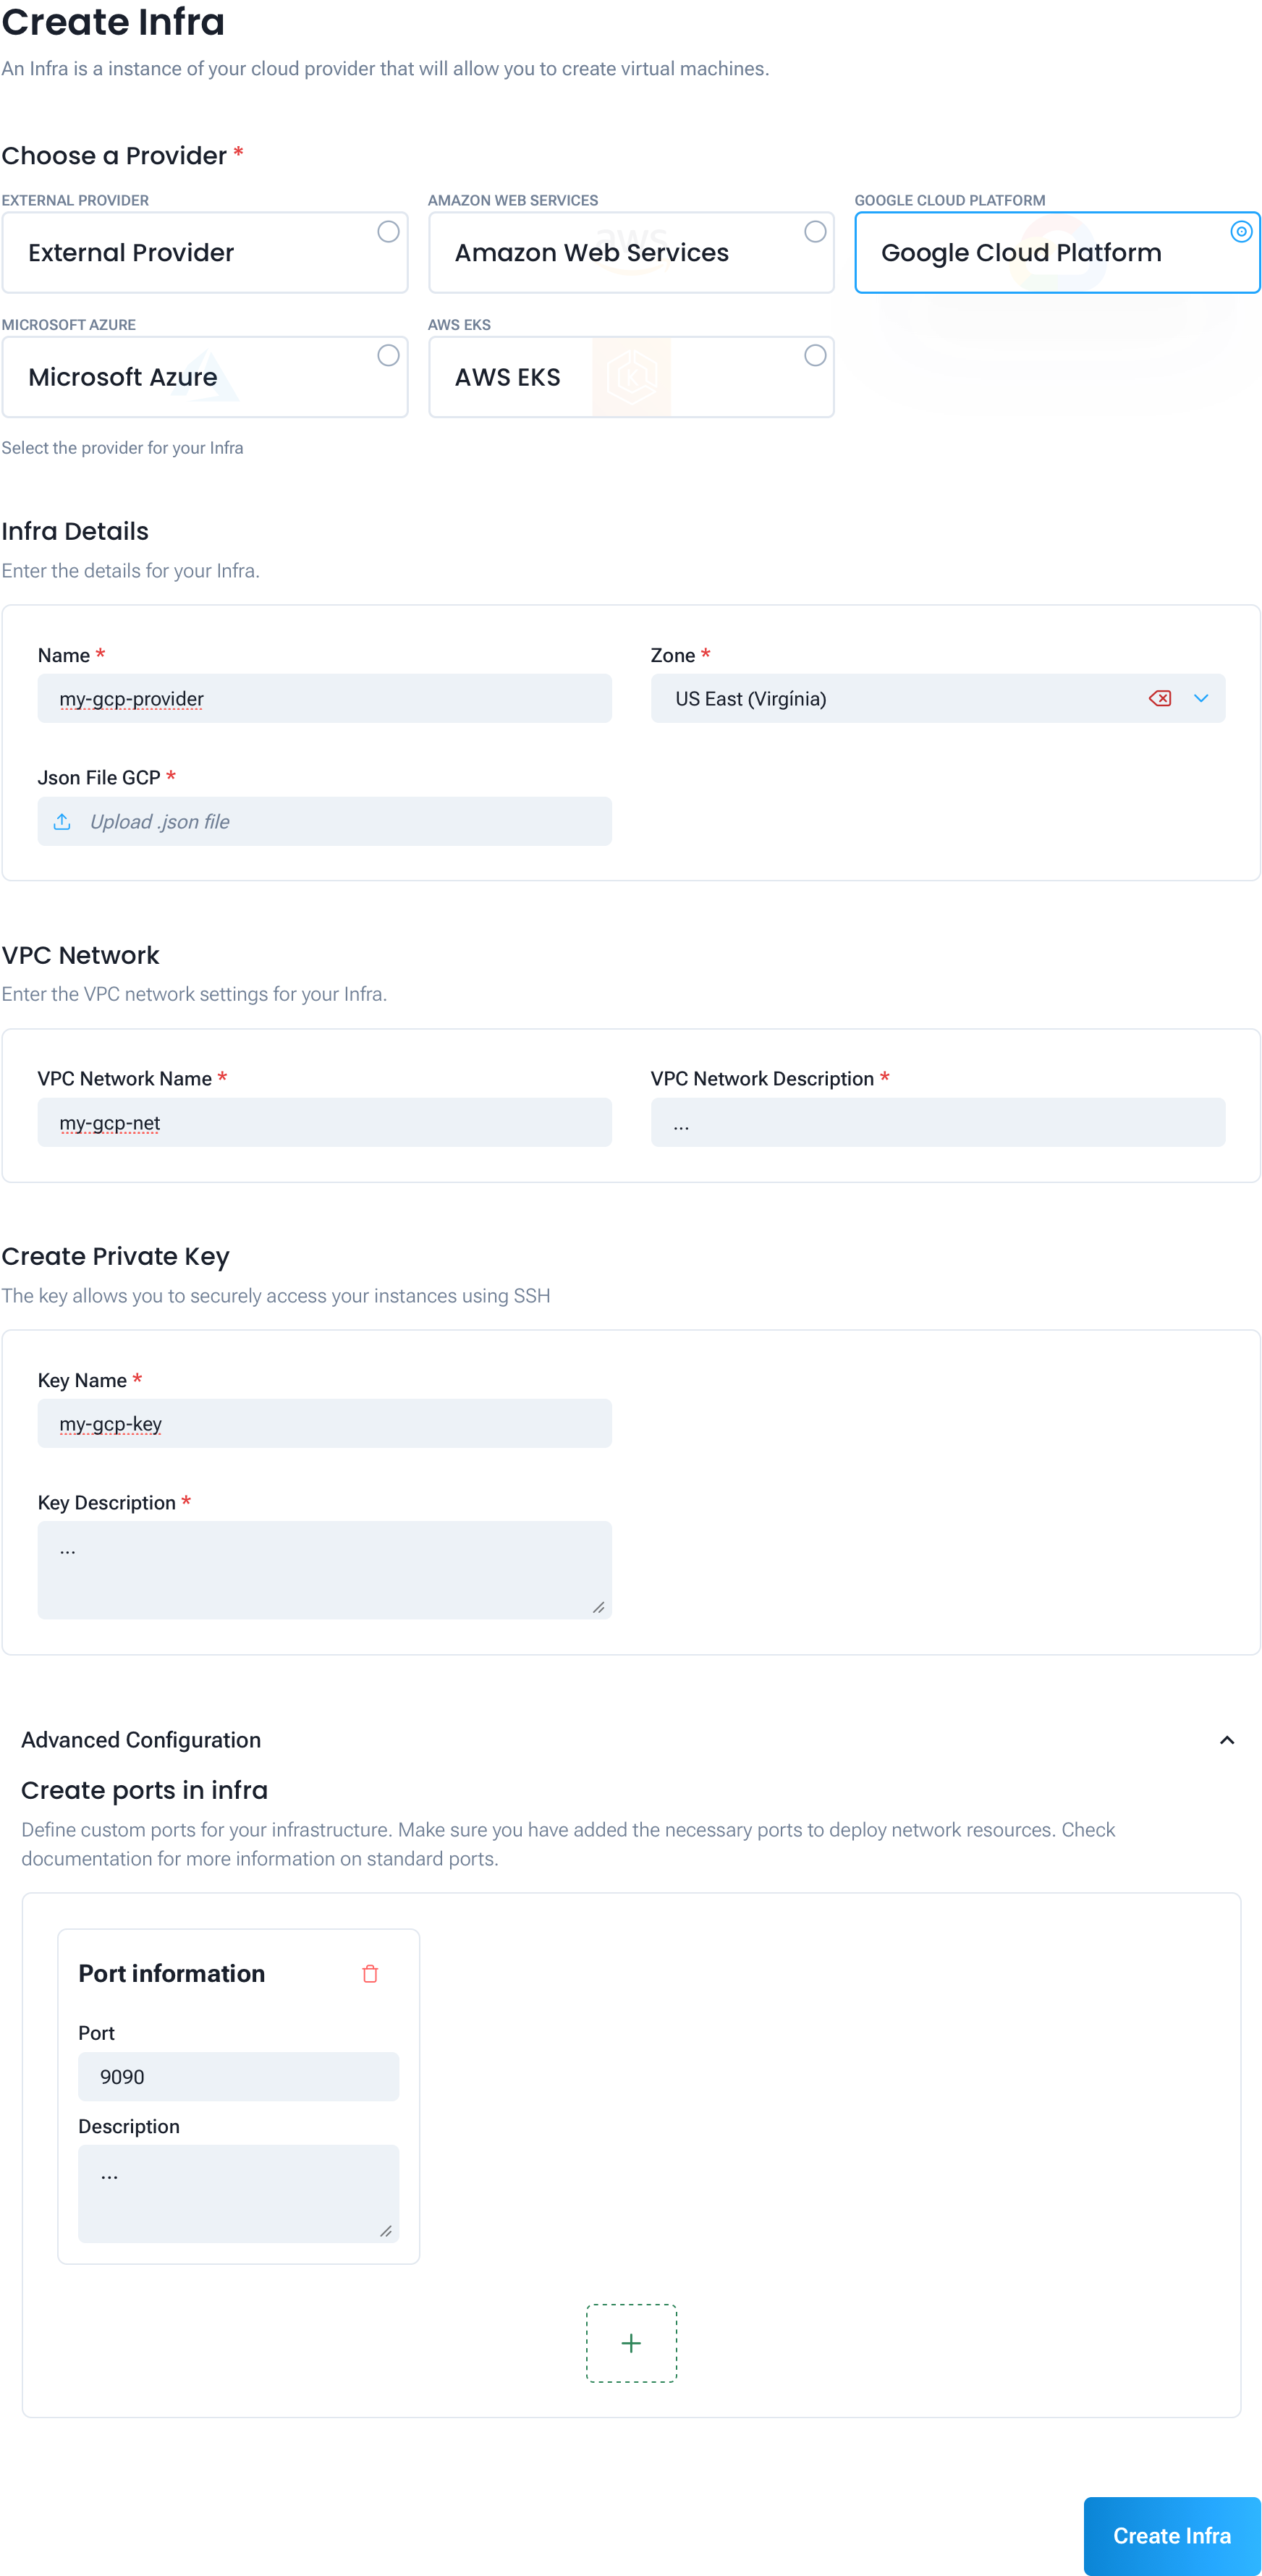
Select Google Cloud Platform and fill in the following:
Infra Details
- Name (required): A name to identify your infrastructure.
- Zone (required): The GCP zone where your VMs will be created (e.g.
us-east1). Select from the dropdown. - Json File GCP (required): Upload your GCP service account JSON key file. This file provides GoInfra with the credentials it needs to provision resources in your Google Cloud project.
VPC Network
- VPC Network Name (required): The name of the VPC network GoInfra will create for your infrastructure.
- VPC Network Description (required): A short description for the VPC network.
Create Private Key
- Key Name (required): The name of the SSH key GoInfra will create to access your instances.
- Key Description (required): A short description for the key.
Open ports
- Choose what will run on the virtual machines, so the firewall opens the right ports. See Choosing the Open Ports.
Then click Create Infra.
After the infra is created, you will be taken to the VM setup step. See the VM Setup Guide for details.
Creating a Microsoft Azure Provider
The Azure provider lets GoInfra create and manage virtual machines within your Azure subscription using an Azure Active Directory app registration.
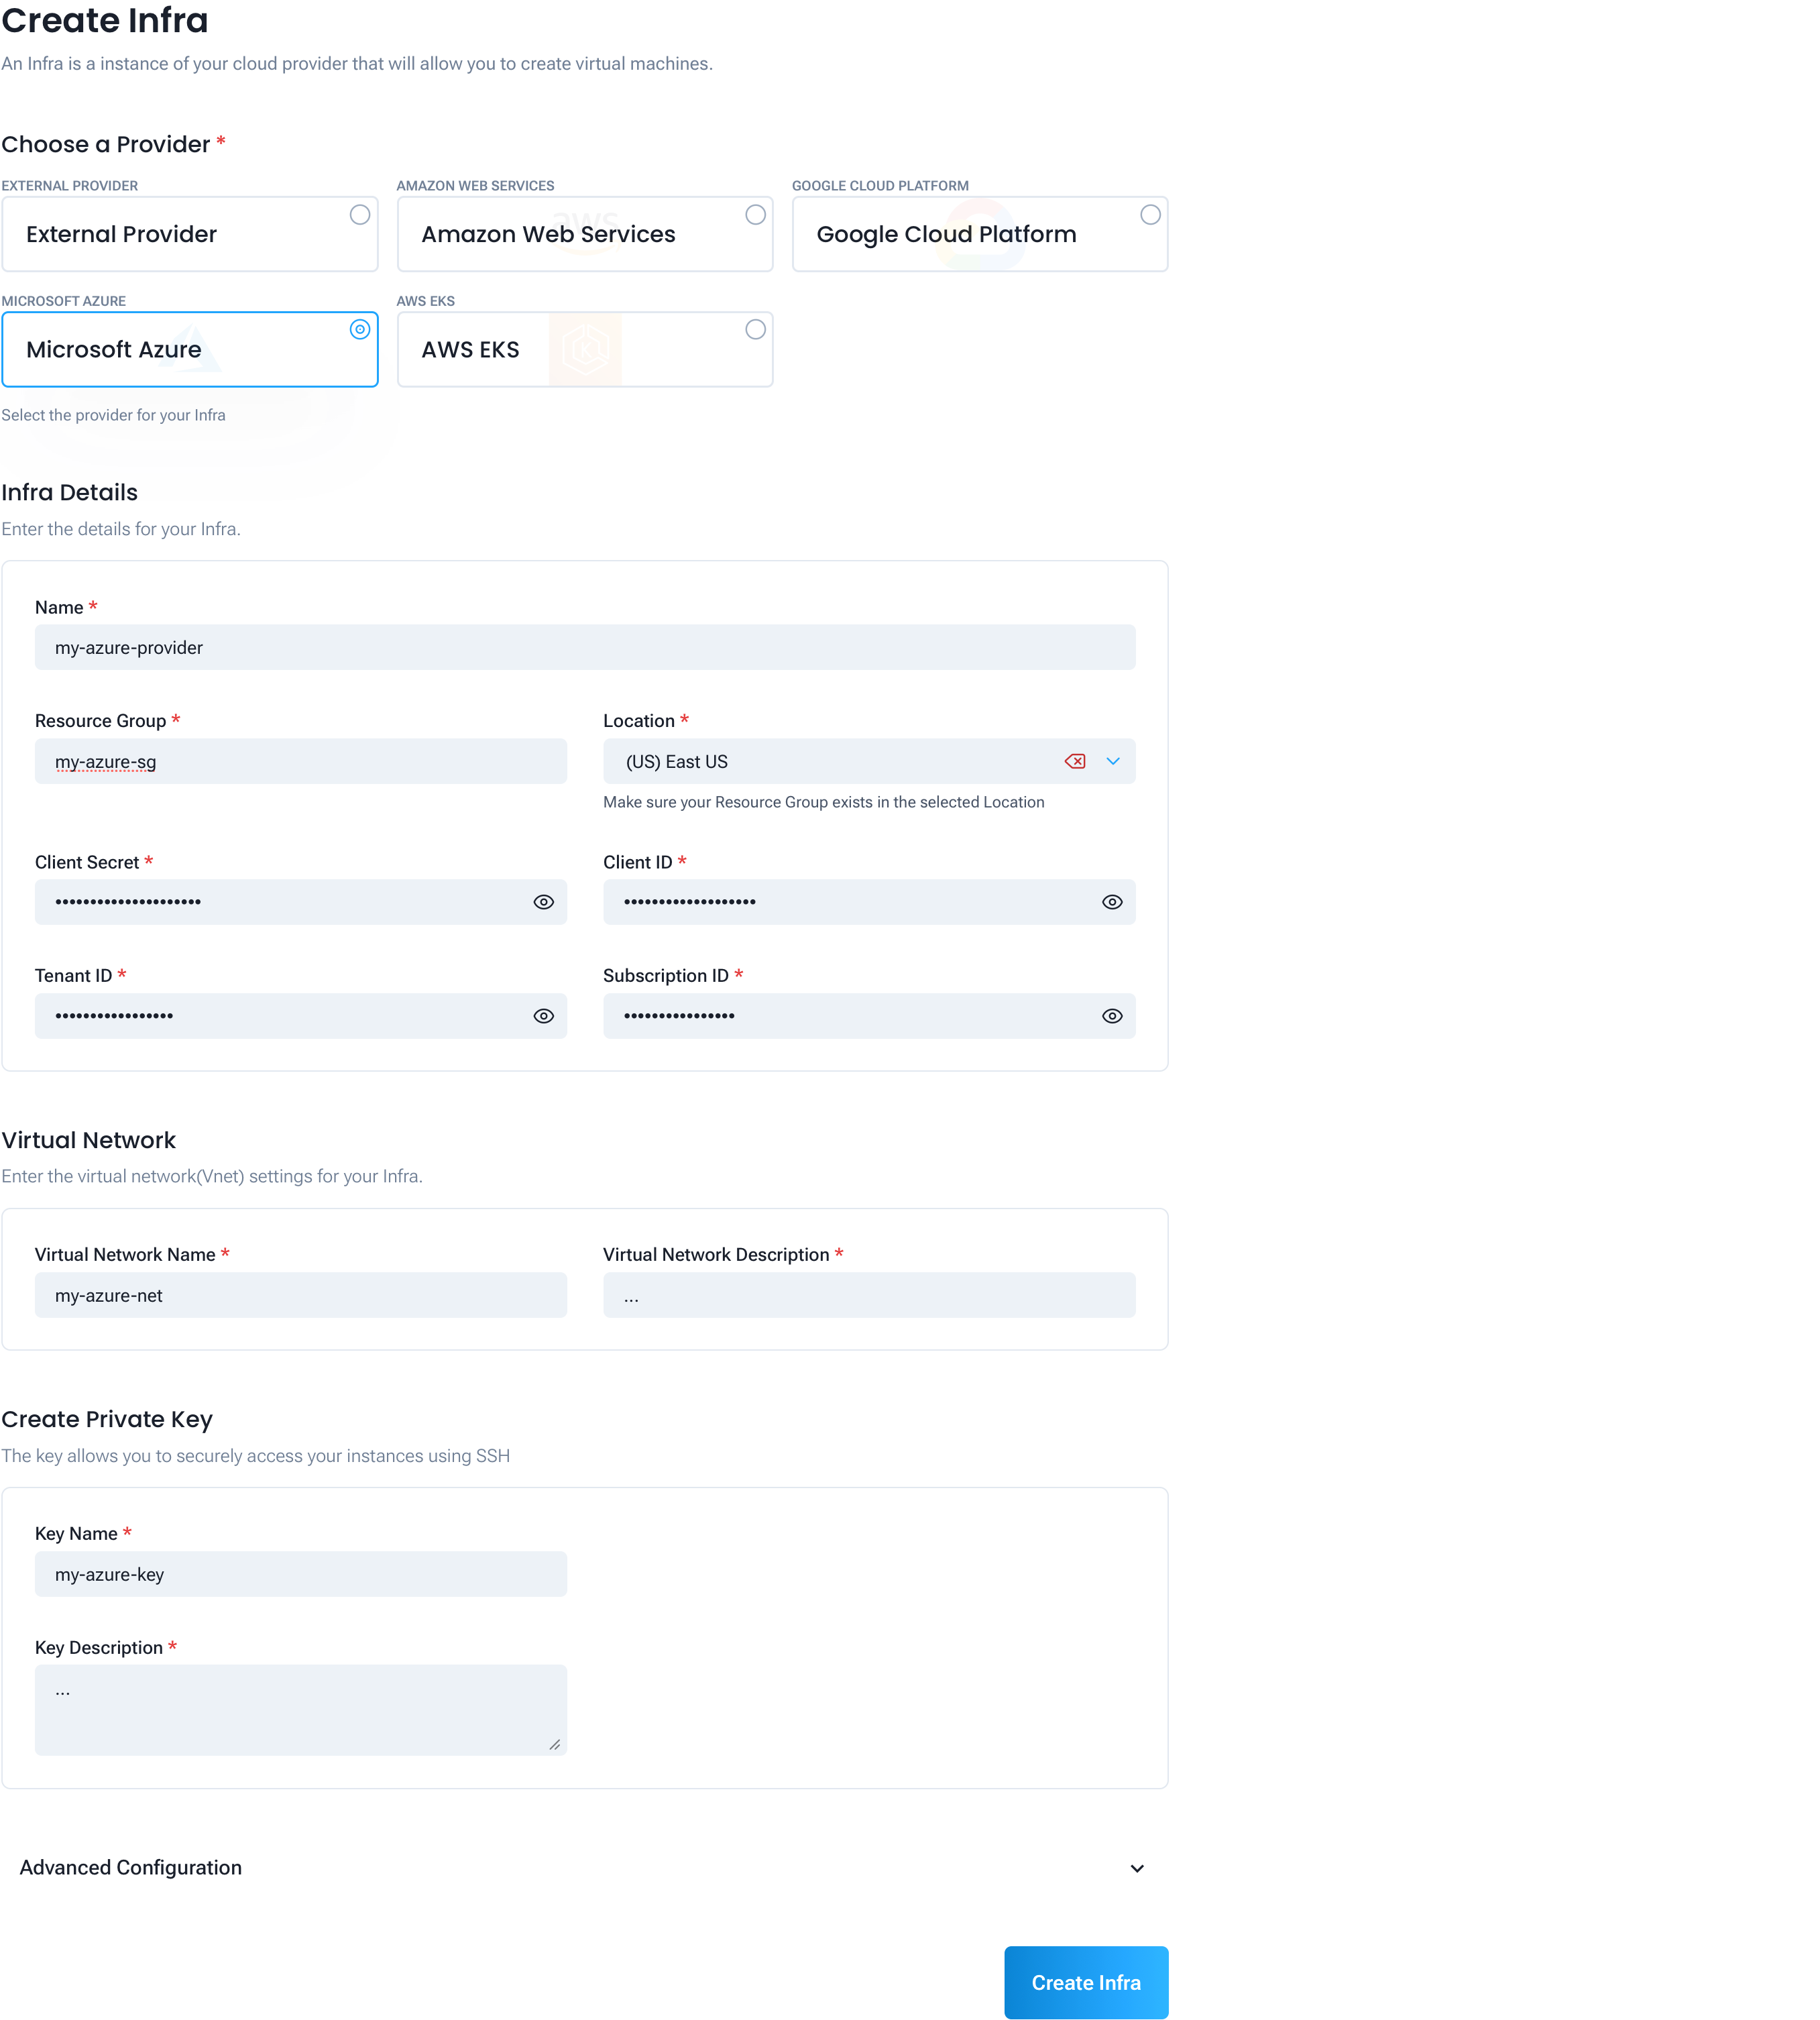
Select Microsoft Azure and fill in the following:
Infra Details
- Name (required): A name to identify your infrastructure.
- Resource Group (required): The name of an existing Azure Resource Group where the infrastructure will be created. Make sure this Resource Group already exists in the selected location.
- Location (required): The Azure region for deployment. Must match the region of the Resource Group above.
- Client Secret (required): The client secret of your Azure Active Directory app registration.
- Client ID (required): The application (client) ID of your Azure AD app registration.
- Tenant ID (required): The directory (tenant) ID of your Azure Active Directory.
- Subscription ID (required): The ID of the Azure subscription where resources will be provisioned.
Virtual Network
- Virtual Network Name (required): The name of the Virtual Network (VNet) GoInfra will create.
- Virtual Network Description (required): A short description for the Virtual Network.
Create Private Key
- Key Name (required): The name of the SSH key GoInfra will create to access your instances.
- Key Description (required): A short description for the key.
Open ports
- Choose what will run on the virtual machines, so the firewall opens the right ports. See Choosing the Open Ports.
Then click Create Infra.
After the infra is created, you will be taken to the VM setup step. See the VM Setup Guide for details.
Creating an AWS EKS Provider
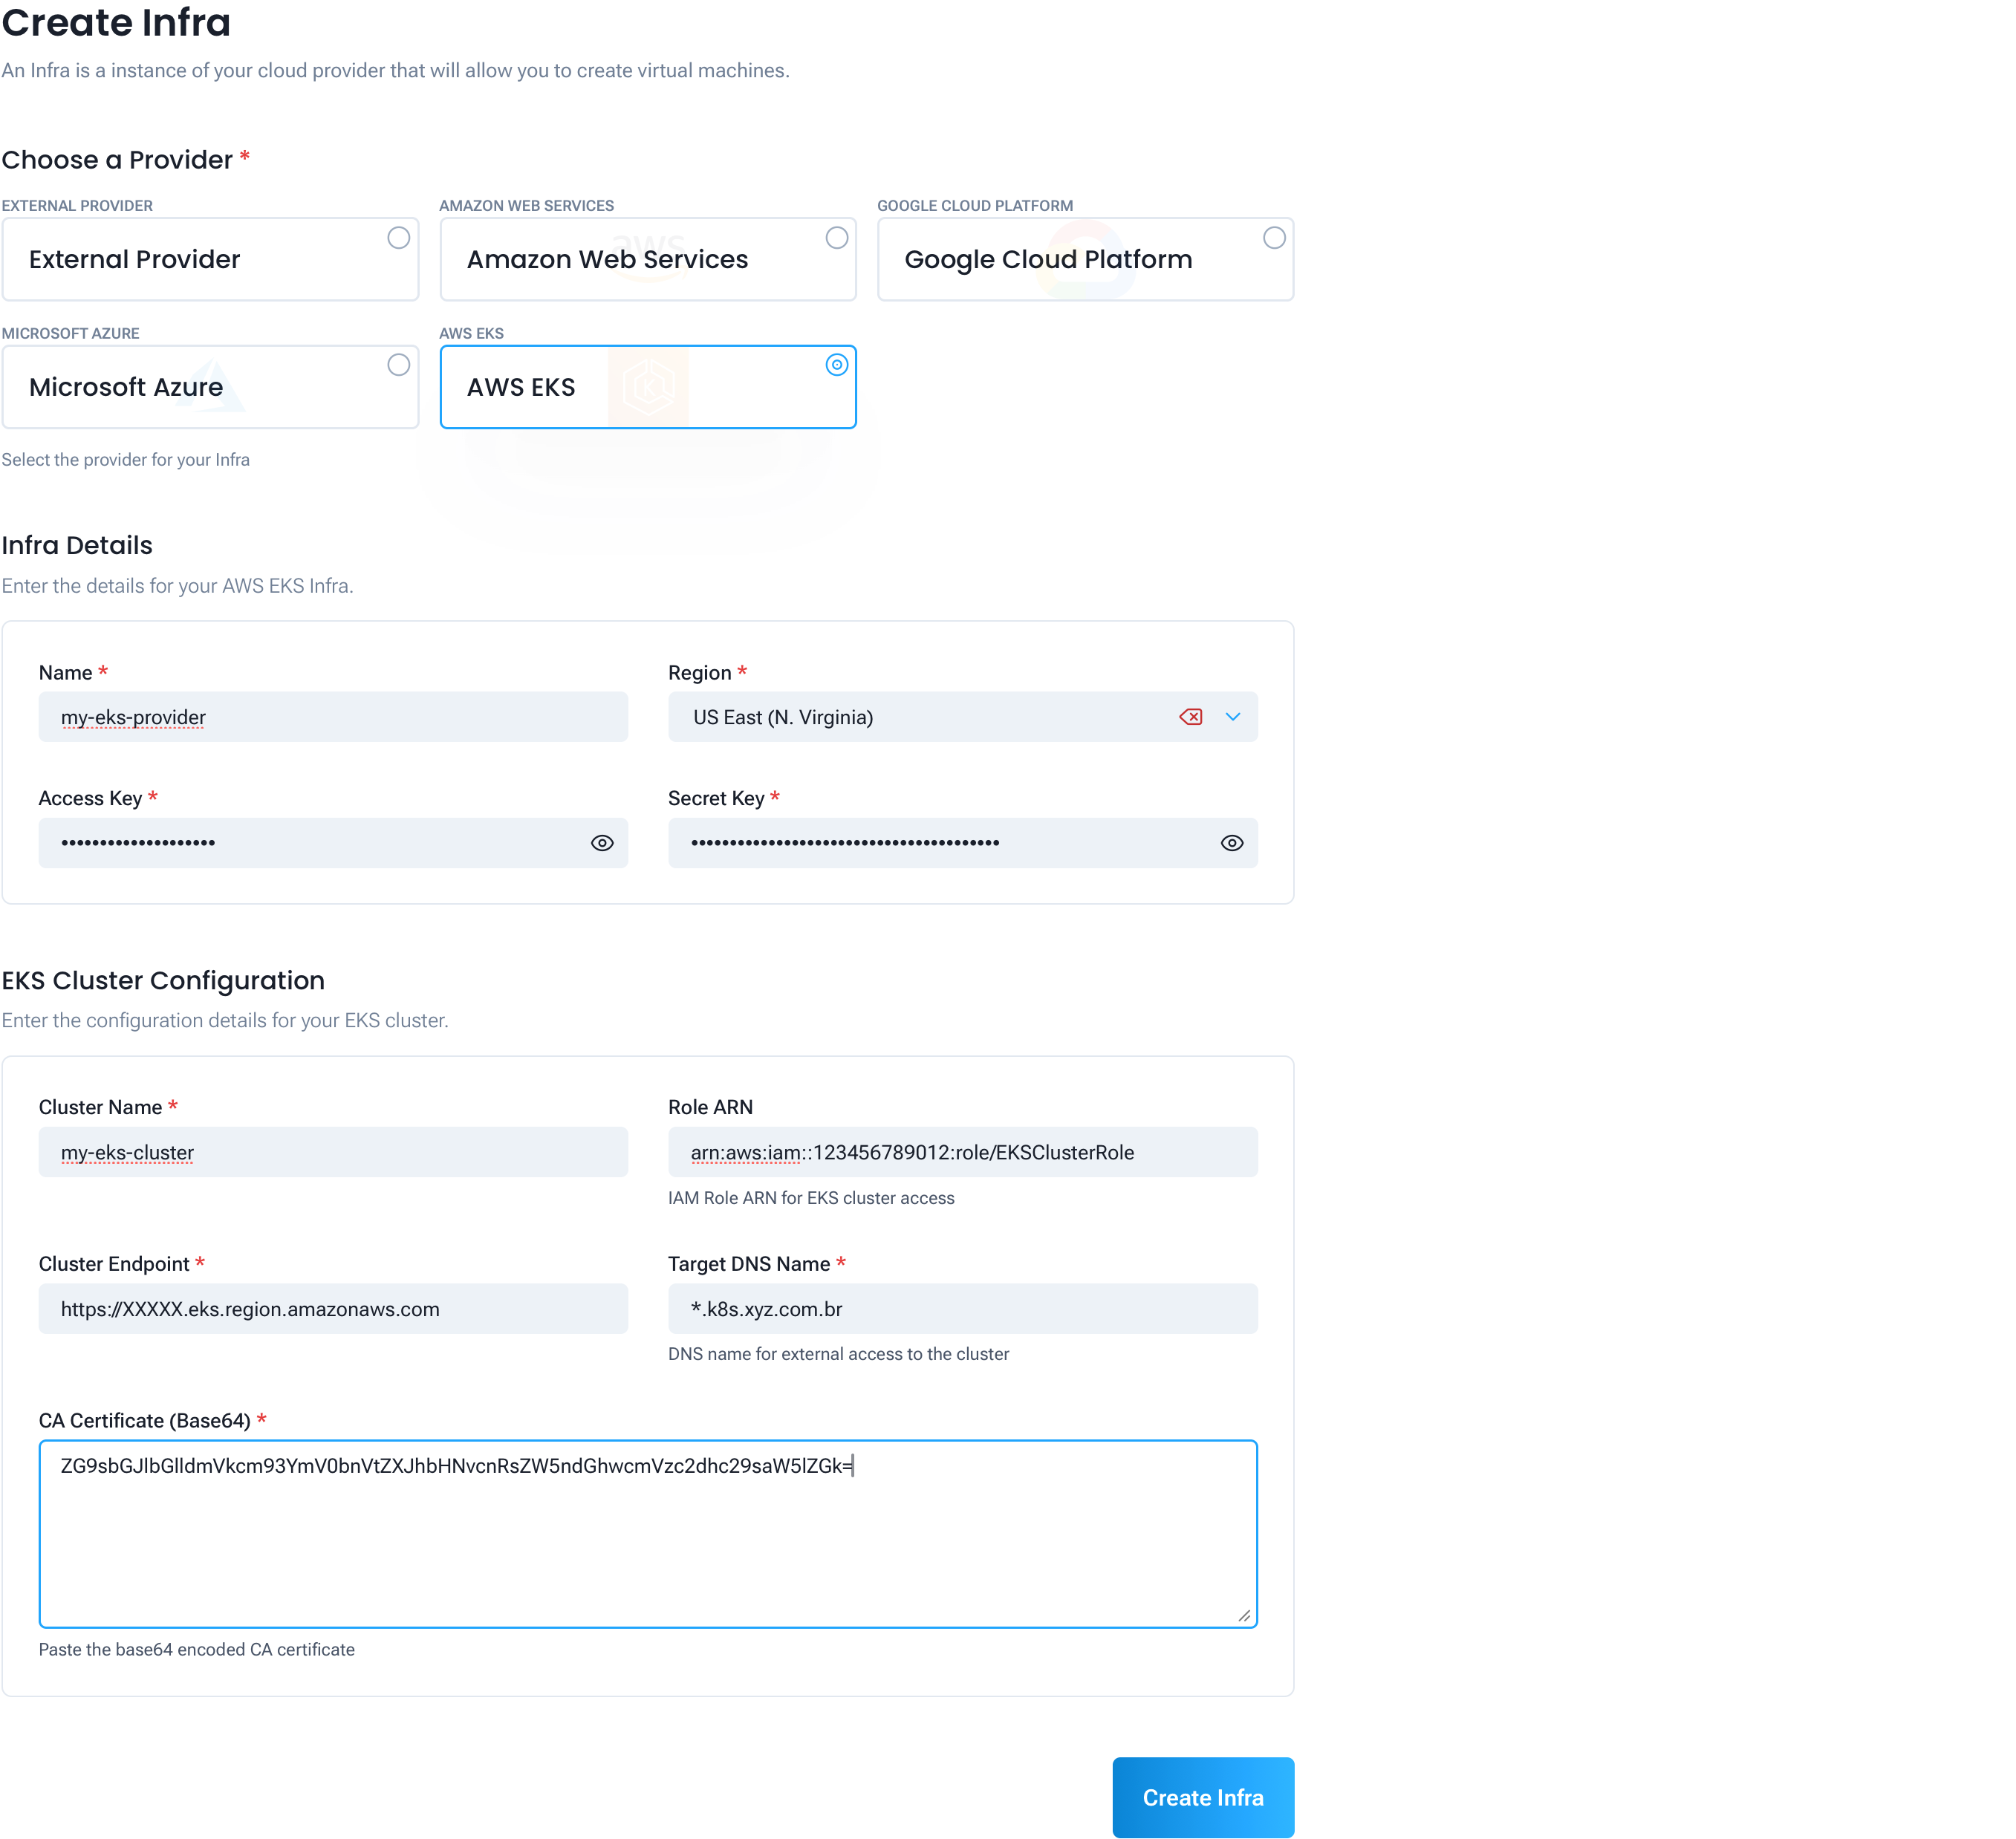
The AWS EKS provider lets GoInfra deploy GoFabric components as pods on an existing Amazon Elastic Kubernetes Service cluster, instead of provisioning individual VMs. GoChain connects to the cluster with a Kubernetes ServiceAccount token that you create and authorize with RBAC; nothing is created in AWS IAM.
Running GoFabric on EKS has its own three-step guide:
- Prepare an EKS cluster — cluster requirements, the namespace and ServiceAccount token, and the values to collect.
- Register an EKS cluster — the AWS EKS form, cluster settings, and rotating the token.
- Deploy on Kubernetes — organizations, sizing, storage and chaincodes.
ℹ️ Note: There is no VM setup step for EKS — blockchain components are deployed directly as Kubernetes pods on your existing cluster.
Choosing the Open Ports
When you create an AWS, GCP or Azure infrastructure, the Open ports section decides which ports the firewall opens on every virtual machine of the Infra. Pick what will run on the machines:
| Preset | Opens |
|---|---|
| Hyperledger Fabric | Peers, orderers, CA, APIs and Chaincode-as-a-Service |
| Hyperledger Besu | RPC, WebSocket, P2P and the ETH API |
| Fabric and Besu | Both platforms on the same machines |
| Custom | Only the ports you add |
The preview lists the rules that will be created, grouped as:
- Always open: 22 (SSH) and 2376 (Docker daemon). GoChain sets up and manages the virtual machines through these ports.
- APIs: 80 (HTTP, used by the CC API and the ETH API).
- Hyperledger Fabric: 7051, 17051, 7052, 5984, 7050, 17050, 9443, 7054, 17054, 8000 (Network API), 8080 (GoInitus), 30999 (Chaincode-as-a-Service), 9090 (Prometheus) and 1695 (Grafana).
- Hyperledger Besu: 8545 (RPC), 8546 (WebSocket), 30303/TCP (P2P) and 30303/UDP (discovery).
Click Customize to copy a preset into an editable list, then use Add port and Remove port. With Custom and no ports added, only the ports GoChain needs are open. Port 443 (HTTPS) is not opened by default; add it if an API uses it.
Managing an Infra
Open an Infra from the GoInfra overview to see its tabs:
- Infra: A summary of the infrastructure. For Kubernetes infras it shows the connection and the cluster settings.
- Keys: The SSH keys of a VM infra.
- Firewall (VM infras): The ports open to the Infra's virtual machines, one card per firewall config, with each rule's port, protocol, source and description. Ports GoChain needs are tagged Required by GoChain, and each card lists the machines that use it. Editing firewall rules and their allowed sources is Coming soon. Infras whose machines were set up on external hosts manage their own firewall, so they have no firewall configs.
- Settings (Kubernetes infras): Cluster settings and Rotate ServiceAccount token. See Managing the Infra.
Next Steps
With your infrastructure created, the next step depends on your provider type:
- External, AWS, GCP, or Azure: Proceed to VM Setup to register or provision the virtual machines for your organization.
- AWS EKS: Your infrastructure is ready. Continue with Deploy on Kubernetes to create your GoFabric organization in the cluster.